
ISO/IEC 27001 is the globally recognized standard for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS).
Unlike single-point security tools, ISO 27001 provides a holistic, risk-based framework to protect data confidentiality, integrity, and availability across people, processes, and technology.
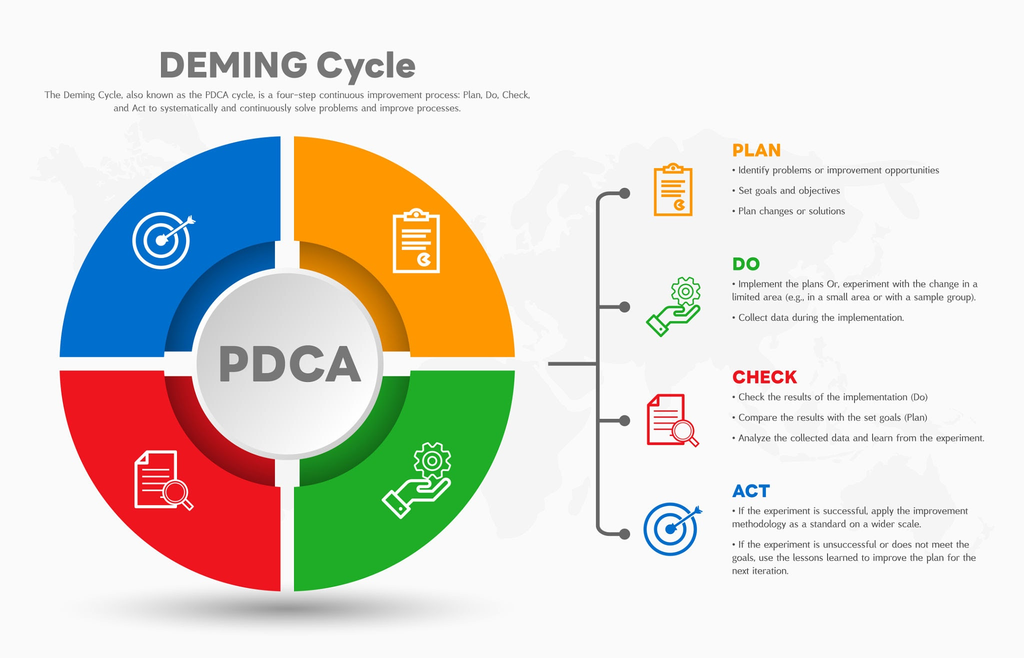
The PDCA continuous improvement cycle governing ISMS implementation. Source: thailerd / Getty Images
Core Structure of ISO 27001
The standard is divided into two primary parts: Management System Clauses (Clauses 4–10) and the Reference Safeguards (Annex A).
1. Mandatory Management Clauses (4–10)
These clauses establish the governance framework required for compliance and certification:
| Clause | Name | Core Requirements |
| Clause 4 | Context of the Organization | Define ISMS scope, internal/external issues, and stakeholder requirements. |
| Clause 5 | Leadership | Secure executive commitment, assign roles, and publish the Information Security Policy. |
| Clause 6 | Planning | Conduct risk assessments, define risk treatment plans, and set security objectives. |
| Clause 7 | Support | Provide required resources, ensure competence, build awareness, and manage documentation. |
| Clause 8 | Operation | Execute operational risk assessment, risk treatment plans, and baseline security processes. |
| Clause 9 | Performance Evaluation | Monitor key metrics, perform internal audits, and hold management reviews. |
| Clause 10 | Improvement | Manage non-conformities, take corrective actions, and continuously improve the ISMS. |
2. Annex A Controls (93 Controls in 4 Themes)
Annex A provides the operational controls tailored to an organization’s specific risk assessment and documented in the Statement of Applicability (SoA):
- Organizational Controls (37 controls): Governance, asset management, cloud security, identity/access management, and incident management.
- People Controls (8 controls): Background screening, terms of employment, remote working, and security awareness training.
- Physical Controls (14 controls): Physical security perimeters, equipment protection, environmental threats, and clear desk policy.
- Technological Controls (34 controls): Cryptography, network security, log monitoring, vulnerability management, and secure coding.
The Certification Lifecycle
[Context & Scope Definition]
            │
            ▼
[Risk Assessment & SoA Draft]
            │
            ▼
[Implement Controls & Policies]
            │
            ▼
[Internal Audit & Management Review]
            │
            ▼
[Stage 1 Audit: Documentation Review]
            │
            ▼
[Stage 2 Audit: Implementation Verification]
            │
            ▼
[Certification Issued (3-Year Cycle with Annual Surveillance Audits)]
Other Source –
YouTube
Make Audit Easy – Austin USA – www.austin.makeauditeasy.com
Make Audit Easy – India – www.makeauditeasy.com
Articles
- 1. Why Organization need ISO 27001
- 2. ISO 27001 Annex A Controls – Organizational Controls (A.5 – 37 controls)
- ISO 27001 Annex A 5.1 Policies for information security
- ISO 27001 Annex A 5.10 Acceptable use of information and other associated assets
- ISO 27001 Annex A 5.11 Return of assets
- ISO 27001 Annex A 5.12 Classification of information
- ISO 27001 Annex A 5.13 Labelling of information
- ISO 27001 Annex A 5.14 Information transfer
- ISO 27001 Annex A 5.15 Access control
- ISO 27001 Annex A 5.16 Identity management
- ISO 27001 Annex A 5.17 Authentication information
- ISO 27001 Annex A 5.18 Access rights – change
- ISO 27001 Annex A 5.19 Information security in supplier relationships
- ISO 27001 Annex A 5.2 Information security roles and responsibilities
- ISO 27001 Annex A 5.20 Addressing information security within supplier agreements
- ISO 27001 Annex A 5.21 Managing information security in the ICT supply chain
- ISO 27001 Annex A 5.22 Monitoring, review and change management of supplier services
- ISO 27001 Annex A 5.23 Information security for use of cloud services
- ISO 27001 Annex A 5.3 Segregation of duties
- ISO 27001 Annex A 5.4 Management responsibilities
- ISO 27001 Annex A 5.5 Contact with authorities
- ISO 27001 Annex A 5.6 Contact with special interest groups
- ISO 27001 Annex A 5.7 Threat intelligence
- ISO 27001 Annex A 5.8 Information security in project management
- ISO 27001 Annex A 5.9 Inventory of information and other associated assets
- ISO 27001 Annex A 5.24 Information security incident management planning and preparation
- ISO 27001 Annex A 5.25 Assessment and decision on information security events
- ISO 27001 Annex A 5.26 Response to information security incidents
- ISO 27001 Annex A 5.27 Learning from information security incidents
- ISO 27001 Annex A 5.28 Collection of evidence
- ISO 27001 Annex A 5.29 Information security during disruption
- ISO 27001 Annex A 5.30 ICT readiness for business continuity
- ISO 27001 Annex A 5.31 Identification of legal, statutory, regulatory and contractual requirements
- ISO 27001 Annex A 5.32 Intellectual property rights
- ISO 27001 Annex A 5.33 Protection of records
- ISO 27001 Annex A 5.34 Privacy and protection of PII
- ISO 27001 Annex A 5.35 Independent review of information security
- ISO 27001 Annex A 5.36 Compliance with policies and standards for information security
- ISO 27001 Annex A 5.37 Documented operating procedures
- 3. ISO 27001 Annex A Controls – People Controls (A.6 – 8 controls)
- ISO 27001 Annex A 6.1 Screening
- ISO 27001 Annex A 6.2 Terms and conditions of employment
- ISO 27001 Annex A 6.3 Information security awareness, education and training
- ISO 27001 Annex A 6.4 Disciplinary process
- ISO 27001 Annex A 6.5 Responsibilities after termination or change of employment
- ISO 27001 Annex A 6.6 Confidentiality or non-disclosure agreements
- ISO 27001 Annex A 6.7 Remote working
- ISO 27001 Annex A 6.8 Information security event reporting
- 4. ISO 27001 Annex A Controls – Physical Controls (A.7 – 14 controls)
- ISO 27001 Annex A 7.1: Physical Security Perimeters
- ISO 27001 Annex A 7.10 Storage media
- ISO 27001 Annex A 7.11 Supporting utilities
- ISO 27001 Annex A 7.12 Cabling security
- ISO 27001 Annex A 7.13 Equipment maintenance
- ISO 27001 Annex A 7.14 Secure disposal or re-use of equipment
- ISO 27001 Annex A 7.2 Physical entry controls
- ISO 27001 Annex A 7.3 Securing offices, rooms and facilities
- ISO 27001 Annex A 7.4 Physical security monitoring
- ISO 27001 Annex A 7.5 Protecting against physical and environmental threats
- ISO 27001 Annex A 7.6 Working in secure areas
- ISO 27001 Annex A 7.7 Clear desk and clear screen
- ISO 27001 Annex A 7.8 Equipment siting and protection
- ISO 27001 Annex A 7.9 Security of assets off-premises
- 5. ISO 27001 Annex A – 8 Technological controls
- ISO 27001 Annex A 8.1 User endpoint devices
- ISO 27001 Annex A 8.10 Information deletion
- ISO 27001 Annex A 8.11 Data masking
- ISO 27001 Annex A 8.12 Data leakage prevention
- ISO 27001 Annex A 8.13 Information backup
- ISO 27001 Annex A 8.14 Redundancy of information processing facilities
- ISO 27001 Annex A 8.15 Logging
- ISO 27001 Annex A 8.16: Monitoring Activities
- ISO 27001 Annex A 8.17 Clock synchronisation
- ISO 27001 Annex A 8.18 Use of privileged utility programs
- ISO 27001 Annex A 8.19 Installation of software on operational systems
- ISO 27001 Annex A 8.2 Privileged access rights
- ISO 27001 Annex A 8.20 Network controls
- ISO 27001 Annex A 8.21 Security of network services
- ISO 27001 Annex A 8.22: Segregation of Networks
- ISO 27001 Annex A 8.23 Web filtering
- ISO 27001 Annex A 8.24 Use of cryptography
- ISO 27001 Annex A 8.25 Secure development lifecycle
- ISO 27001 Annex A 8.26 Application security requirements
- ISO 27001 Annex A 8.27 Secure system architecture and engineering principles
- ISO 27001 Annex A 8.29 Security testing in development and acceptance
- ISO 27001 Annex A 8.3 Information access restriction
- ISO 27001 Annex A 8.30 Outsourced development
- ISO 27001 Annex A 8.32 Change management
- ISO 27001 Annex A 8.33 Test information
- ISO 27001 Annex A 8.34 Protection of information systems during audit and testing
- ISO 27001 Annex A 8.4 Access to source code
- ISO 27001 Annex A 8.5 Secure authentication
- ISO 27001 Annex A 8.6 Capacity management
- ISO 27001 Annex A 8.7 Protection against malware
- ISO 27001 Annex A 8.8 Management of technical vulnerabilities
- ISO 27001 Annex A 8.9 Configuration management
- SO 27001 Annex A 8.31 Separation of development, test and production environments
- Other Doc
- Example: AWS SaaS Startup
- ISO 27001 Risk Assessment Guide
- How to Prepare an ISO 27001 Statement of Applicability — AWS SaaS Startup Example
- ISO 27001 Statement of Applicability (SoA) Guide
- ISO 27001 Implementation Guide for Startups
- ISO 27001 Implementation Guide for Startups
- ISO 27001 Internal Audit Checklist
- ISO 27001 RACI Matrix
- ISO 27001 Risk Assessment Guide
- ISO 27001 Roles & Responsibilities Template
- ISO 27001 Access Control Policy
- Segregation of Duties Policy