
Illustrative relative need for ISO 27001 based on customer requirements, sensitivity of data, regulatory expectations, and business risk.0/102.5/105/107.5/1010/10Defence & GovernmentBanking & FinTechCloud & SaaSHealthcare & Heal…IT Services & BPOTelecomData Centers & MSPsE-commerceLegal & ConsultingManufacturingHR & PayrollEducation & EdTech
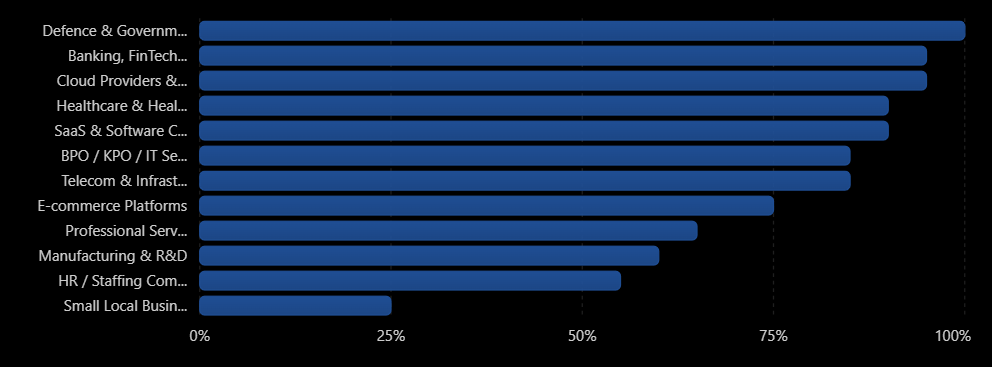
| Industry / Company Type | Need for ISO 27001 | Main Reason |
|---|---|---|
| Defence, Government, PSU | Very High | Sensitive and national data |
| Banking, FinTech, Insurance | Very High | Financial information and regulations |
| SaaS, Cloud, Software Companies | High | Enterprise customer requirements |
| Healthcare, HealthTech | High | Patient and health data |
| IT Services, BPO, KPO | High | Client data processing |
| Data Centers, MSPs | High | Access to customer systems |
| Telecom | High | Large-scale data handling |
| E-commerce | Medium–High | Customer and payment data |
| Legal, Consulting, CA Firms | Medium–High | Confidential client information |
| Manufacturing | Medium | IP and supply chain security |
| HR, Payroll Companies | Medium | Employee personal data |
| Education, EdTech | Medium | Student information |
Simple Rule
Organizations generally need ISO 27001 when they:
- Handle sensitive information
- Process customer data
- Sell to enterprise or international clients
- Work in regulated industries
- Need to prove their security practices to customers
ISO 27001 is most commonly adopted by SaaS, IT Services, BFSI, Healthcare, BPO, Cloud, Telecom, Defence, Government, and companies serving global customers.