
ISO/IEC 27001 Annex A serves as the practical checklist of information security safeguards—known as controls—that an organization can implement to manage cyber and data security risks.
While Clauses 4 through 10 of ISO 27001 define the governance requirements for an Information Security Management System (ISMS), Annex A provides the specific operational measures used to protect the confidentiality, integrity, and availability of information.
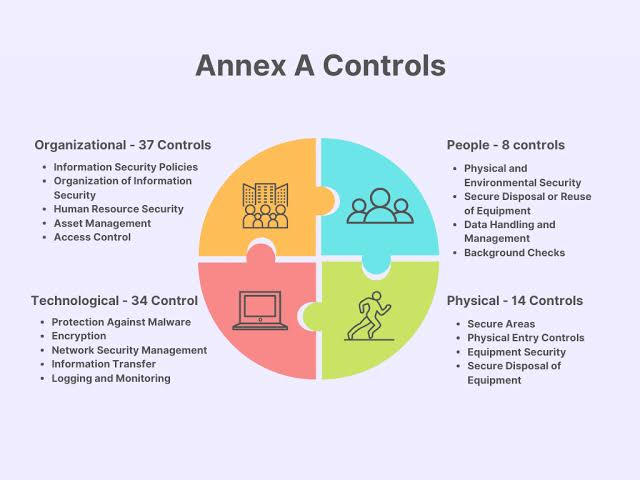
Under the ISO/IEC 27001 framework, the controls are structured across four operational themes comprising 93 controls in total:
- Organizational Controls (A.5 – 37 controls): High-level operational practices, including security policies, asset management, access governance, threat intelligence, and cloud service security.
- People Controls (A.6 – 8 controls): Human resource safety measures, such as background checks, security awareness training, remote work guidelines, and offboarding procedures.
- Physical Controls (A.7 – 14 controls): Measures protecting physical spaces and equipment, including perimeter security, entry controls, clear desk/screen policies, and equipment maintenance.
- Technological Controls (A.8 – 34 controls): Technical defenses, such as data encryption, network security, secure coding practices, vulnerability management, and log monitoring.
Organizations select relevant Annex A controls based on their internal risk assessment, documenting which controls are applied (and justifying any exclusions) within their formal Statement of Applicability (SoA)
Articles
- ISO 27001 Annex A 5.1 Policies for information security
- ISO 27001 Annex A 5.10 Acceptable use of information and other associated assets
- ISO 27001 Annex A 5.11 Return of assets
- ISO 27001 Annex A 5.12 Classification of information
- ISO 27001 Annex A 5.13 Labelling of information
- ISO 27001 Annex A 5.14 Information transfer
- ISO 27001 Annex A 5.15 Access control
- ISO 27001 Annex A 5.16 Identity management
- ISO 27001 Annex A 5.17 Authentication information
- ISO 27001 Annex A 5.18 Access rights – change
- ISO 27001 Annex A 5.19 Information security in supplier relationships
- ISO 27001 Annex A 5.2 Information security roles and responsibilities
- ISO 27001 Annex A 5.20 Addressing information security within supplier agreements
- ISO 27001 Annex A 5.21 Managing information security in the ICT supply chain
- ISO 27001 Annex A 5.22 Monitoring, review and change management of supplier services
- ISO 27001 Annex A 5.23 Information security for use of cloud services
- ISO 27001 Annex A 5.3 Segregation of duties
- ISO 27001 Annex A 5.4 Management responsibilities
- ISO 27001 Annex A 5.5 Contact with authorities
- ISO 27001 Annex A 5.6 Contact with special interest groups
- ISO 27001 Annex A 5.7 Threat intelligence
- ISO 27001 Annex A 5.8 Information security in project management
- ISO 27001 Annex A 5.9 Inventory of information and other associated assets
- ISO 27001 Annex A 5.24 Information security incident management planning and preparation
- ISO 27001 Annex A 5.25 Assessment and decision on information security events
- ISO 27001 Annex A 5.26 Response to information security incidents
- ISO 27001 Annex A 5.27 Learning from information security incidents
- ISO 27001 Annex A 5.28 Collection of evidence
- ISO 27001 Annex A 5.29 Information security during disruption
- ISO 27001 Annex A 5.30 ICT readiness for business continuity
- ISO 27001 Annex A 5.31 Identification of legal, statutory, regulatory and contractual requirements
- ISO 27001 Annex A 5.32 Intellectual property rights
- ISO 27001 Annex A 5.33 Protection of records
- ISO 27001 Annex A 5.34 Privacy and protection of PII
- ISO 27001 Annex A 5.35 Independent review of information security
- ISO 27001 Annex A 5.36 Compliance with policies and standards for information security
- ISO 27001 Annex A 5.37 Documented operating procedures